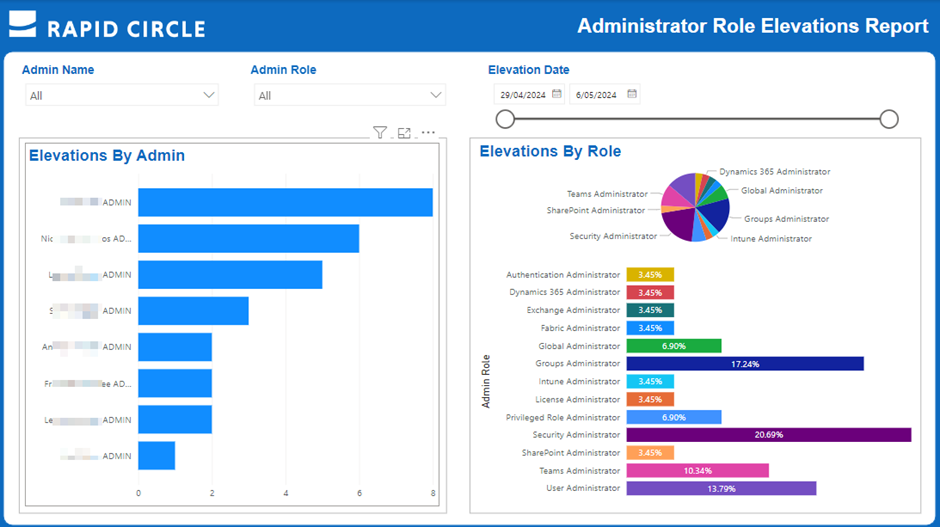
Privileged Identity Management (PIM) in Entra ID (formerly known as Azure Active Directory) is a fantastic solution for helping reduce overuse of administrative rights by IT admins in the course of administering Microsoft 365 environments. All too-often, IT admins will perform functions using their admin account using the Global Administrator because, quite frankly, it’s easier.…… Continue reading A better way to report administrator role elevations in Privileged Identity Management
Tag: AAD
Windows 10 & Azure AD challenge after de-federation
Just a quick post on a quick fix. Recently at ████████████ we removed de-federated our ADFS infrastructure from Office 365 as it was no longer required. After running the PowerShell scripts to switch our domain back to Managed (from Federated), forcing Yammer to use Office 365 identities (as it overrides the SSO configuration in the process),…… Continue reading Windows 10 & Azure AD challenge after de-federation
Unable to change passwords after deactivation of DirSync
We came across an interesting issue recently with a tenant after deactivating DirSync. The issue was that users could not change their own passwords in Office 365, and were given the following error message: “Sorry, you can’t change your password here. Follow the steps recommended by your organization or ask your admin for help.” This…… Continue reading Unable to change passwords after deactivation of DirSync